Protect the systems your operation depends on
Cybersecurity services for the networks, devices and control systems behind industrial operations. Understand your exposure, strengthen access and improve your ability to recognise and respond to cyber threats, with operational requirements at the centre.
Cyber risk becomes operational risk
Industrial systems connect people, equipment and processes. Those connections also create pathways that need to be understood and protected. We help your team examine how systems communicate, who can access them and where security weaknesses could affect operations.
Start with a clearer picture. Build a practical path toward stronger protection.
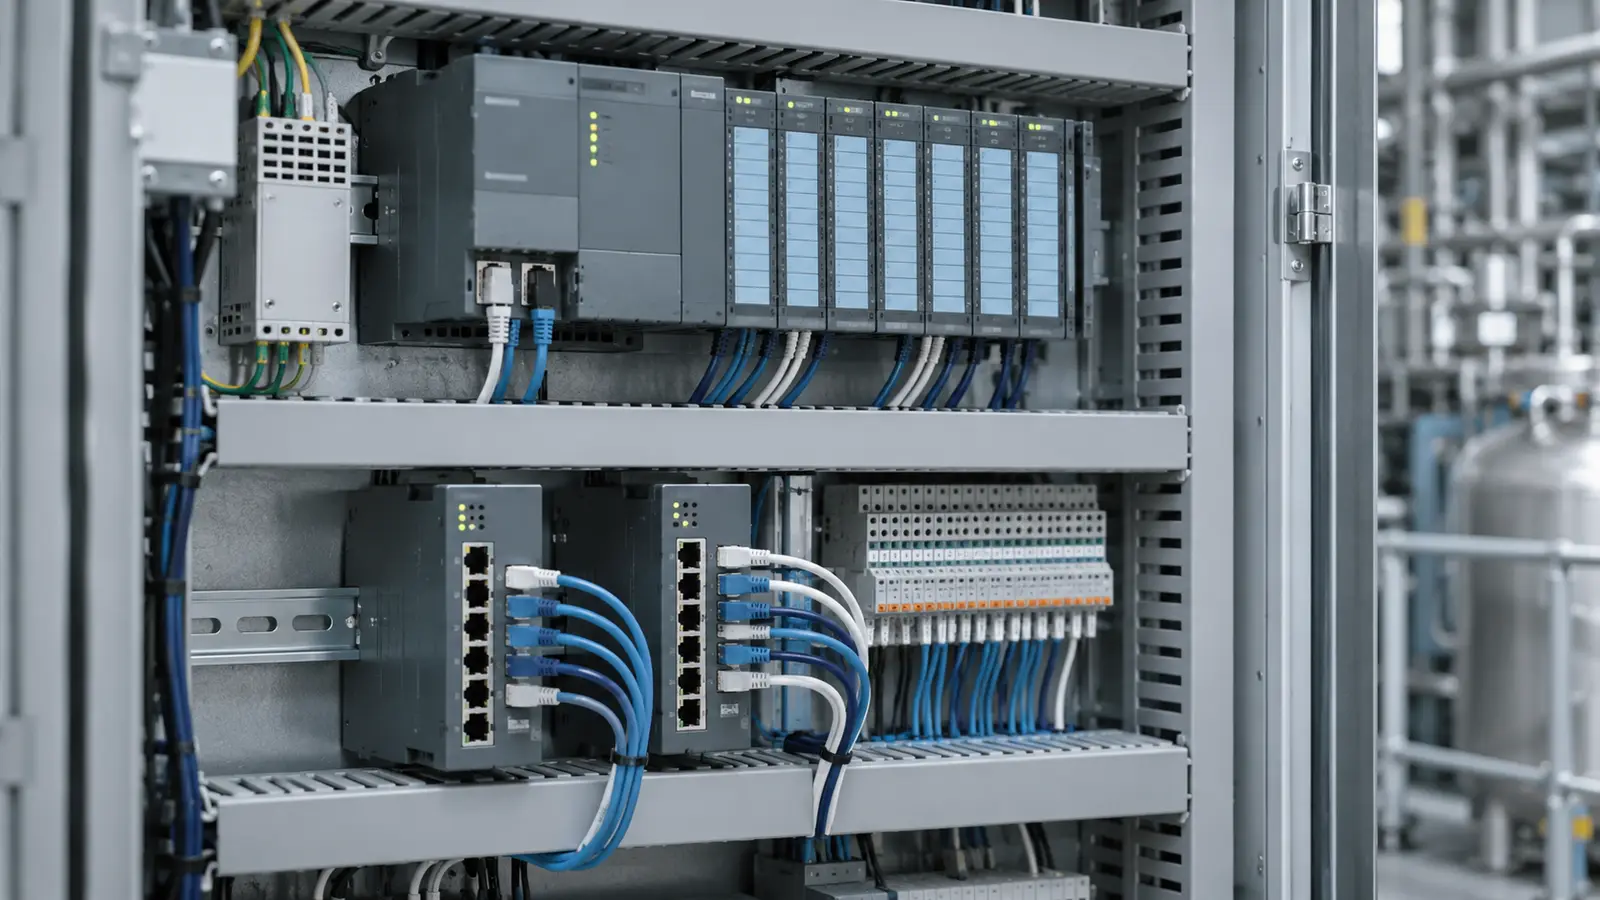
First, understand what is connected
Effective protection starts with visibility into your assets and their role in the operation.
- OT asset visibilityBuild an inventory of industrial devices, systems and relevant connections.
- Network and communication mappingUnderstand how information moves between operational systems, enterprise networks and external services.
- Operational criticalityIdentify which assets support essential processes and where disruption would have the greatest impact.
The outcomeA clearer view of what needs protection and where to focus first.
Then, examine the paths into your operation
Access should reflect the work someone needs to perform, and the systems they are authorised to reach.
- Remote and vendor accessReview how employees, suppliers and maintenance providers connect to operational systems.
- Network segmentationAssess boundaries between enterprise IT, operational networks and critical equipment environments.
- Identity and permissionsReview accounts, privileges, authentication and access responsibilities.
- Configuration and exposureIdentify unnecessary connections, insecure settings and potential exposure points.
The outcomePrioritised recommendations for strengthening access and reducing avoidable exposure.
Recognise changes that deserve investigation
A new device, an unexpected connection or unusual access activity can create questions your team needs to answer. OT security monitoring helps bring relevant observations into view, alongside the context needed for investigation.
- Unexpected connectionsIdentify communication that differs from the approved or established network pattern.
- Unusual access activityReview unexpected login behaviour, remote sessions and access to sensitive systems.
- Asset and configuration changesSurface relevant changes to monitored devices and configurations where suitable data is available.
- Security event notificationsRoute observations to designated contacts through agreed dashboards and communication channels.
Monitoring coverage is defined around your systems, available data and operational requirements.
Turn findings into a practical security plan
A list of weaknesses is useful only when your team knows what to do next. We prioritise findings by their operational significance, exposure and remediation requirements.
- Address the highest-priority risksFocus on issues that could have the greatest effect on critical systems and processes.
- Plan changes around operationsConsider equipment constraints, vendor requirements, maintenance windows and change-control procedures.
- Prepare for an incidentDefine responsibilities, escalation paths and response procedures before an event demands them.
- Review recovery readinessAssess backup arrangements, restoration procedures and the information needed to support recovery.
The outcomeAn actionable improvement plan with clear priorities and ownership.
Security that understands the operating environment
Industrial cybersecurity needs to account for the systems already in service and the work they support. Our approach starts with your environment: its equipment, architecture, dependencies and operating constraints.
- 01 / Understand
Establish the environment.
Identify assets, connections, responsibilities and operational priorities.
- 02 / Assess
Examine the exposure.
Review access controls, network boundaries and monitoring gaps.
- 03 / Strengthen
Prioritise improvement.
Develop an improvement plan and support agreed security measures.
- 04 / Prepare
Connect the response.
Build monitoring, escalation and response arrangements around your team.
Frameworks we work to
Assessments and improvement plans are structured around recognised industrial and national guidance, so your findings map onto the language your auditors, regulators and engineers already use.
- IEC 62443Security for industrial automation and control systems. We use its ideas of zones and conduits and security levels to structure the review of network boundaries and access.
- NIST SP 800-82 Rev. 3The NIST Guide to OT Security, used as a reference for the risks and safeguards that suit operational technology.
- NIST Cybersecurity Framework 2.0Our four steps line up with its functions: understand and assess map to Identify, strengthen to Protect, recognise to Detect, and prepare to Respond and Recover.
- UK NCSC Cyber Assessment FrameworkAssessments can be aligned with the CAF, with the NIS Regulations 2018 and the EU NIS2 Directive in mind for operators of essential services. We help you prepare evidence for that work.
- ISO/IEC 27001Where OT connects to your enterprise information security management system, we link findings to it.
- MITRE ATT&CK for ICSUsed to make monitoring threat-informed, by describing how attackers are known to act against industrial control systems.
Passive first, no disruption to running processes
Industrial systems are already in service, so we start by looking, not touching.
- Non-intrusive discoveryWe begin with passive observation and the information you already hold, so running processes are not disturbed.
- Change windowsAnything that could affect operations is planned for agreed maintenance windows and your change-control procedures.
- Vendor coordinationEquipment vendors are involved where their support terms or system constraints apply.
Naming a framework here is not a claim of certification against it, and working to one does not make your organisation compliant. Compliance decisions rest with your auditor or regulator.
A broader view of industrial protection
Different services address different sources of industrial risk.
- 03 / Security
OT Cybersecurity
Protect the digital systems and connections supporting the operation.
Common questions about this work
What does OT cybersecurity cover for an industrial site?
It protects the networks, devices and control systems that run the process. Work starts with passive discovery of what is connected, then reviews remote and vendor access, segmentation and permissions, monitors for unexpected changes and turns findings into a prioritised plan structured around IEC 62443, NIST SP 800-82 and the NCSC CAF.
Keep reading related pages
- Video AI and vision agentsVision agents that watch camera feeds and alert the right person.
- Physical AI for equipmentSensor intelligence that spots when equipment behaviour changes.
- AI consultingPick the use case and the simplest design before building.
- Security overviewTenant isolation, access, audit and how agents are kept in bounds.
Where does your OT environment need greater clarity?
Start with an assessment, a remote-access concern or a critical system you want to protect.